IT takes the blame for missed milestones, but the business owns the decisions that caused them.
An independent review gives you the evidence you need to get business issues addressed – before they become your problem.
The root cause problem
Program failures are rarely single-cause. Business readiness gaps, sponsorship quality, resourcing decisions, and timeline commitments made outside IT’s authority or visibility all contribute to program outcomes, and every area is incentivised to report optimistically until the program fails. Without external evidence, the board sees only the milestone that was missed — not the upstream decisions that made it unmeetable.
Post-mortems rarely resolve this. They happen after the damage is done and tend toward blame attribution rather than root-cause analysis. By the time a report is commissioned, the business has decided who is to blame and the scope is shaped to reach an ‘outcome’. Arguing in steering committees that business-side decisions are the real constraint sounds defensive when a failure has already occurred and been attributed, and this undermines any argument you make.
An independent review, fast enough to be commissioned at a stage-gate or at the first suspicion of a problem, lets you pinpoint problems and gives you the evidence to argue for solutions before they become a ‘delivery’ failure. Where you flag a resourcing risk and the Sponsor rates it green, that divergence is documented in the alignment index at the time, without attributing to a role or individual. For example, where decisions aren’t made in time for implementation, this is flagged as a risk. This gives you the opportunity to save the business from themselves, and protect yourself at the same time.
What the diagnostic covers
The diagnostic assesses 16 risk dimensions — business readiness, sponsorship, change and communications, resourcing, vendor management, dependency management, and technology execution among them. This is not an IT audit – it examines all contributing factors, including those that originate outside the technology function.
Two output modes serve different audiences:
Board View (default): 6-8 board-relevant dimensions — risk rating, confidence, benchmark percentile, and conditions-to-proceed. Designed for upward reporting to the committee
Delivery View (optional): All 16 dimensions with full operational detail. Designed for intervention planning at the operational level
You control which view is provided to which audience. Board View goes upward. Delivery View stays where it drives action. The diagnostic benchmarks programs, not people — the Alignment Index surfaces divergence without individual attribution.
Portfolio standardisation
Ad-hoc assurance reviews produces non-comparable outputs — different scope, different methodology, different quality at every gate, making it hard to assess portfolio-level risk when every program has been assessed on different terms.
ProjectPhD applies one methodology consistently at every material stage gate, producing comparable outputs across every program. This gives you benchmarked data and trend analysis in a standardised format — external evidence, not internally-generated reporting assembled by the teams being assessed.
When embedded as a standing control across the portfolio, the diagnostic gives you something no amount of internal reporting can provide: a consistent governance language for the board that is independently sourced, comparable across programs, and not subject to the credibility discount that IT-generated reporting carries.
A Portfolio Subscription extends this to a portfolio-level view: heatmap, trend, and watchlist data across all material programs.
Enterprise controls
The diagnostic is built for enterprise security and procurement requirements:
- Data residency options (AU, US, EU)
- Defined retention controls and deletion protocols
These address the operational friction that blocks adoption at enterprise scale. Deploying a standard diagnostic across the portfolio should not require a security exception at every gate.
20-Year Empirical Record
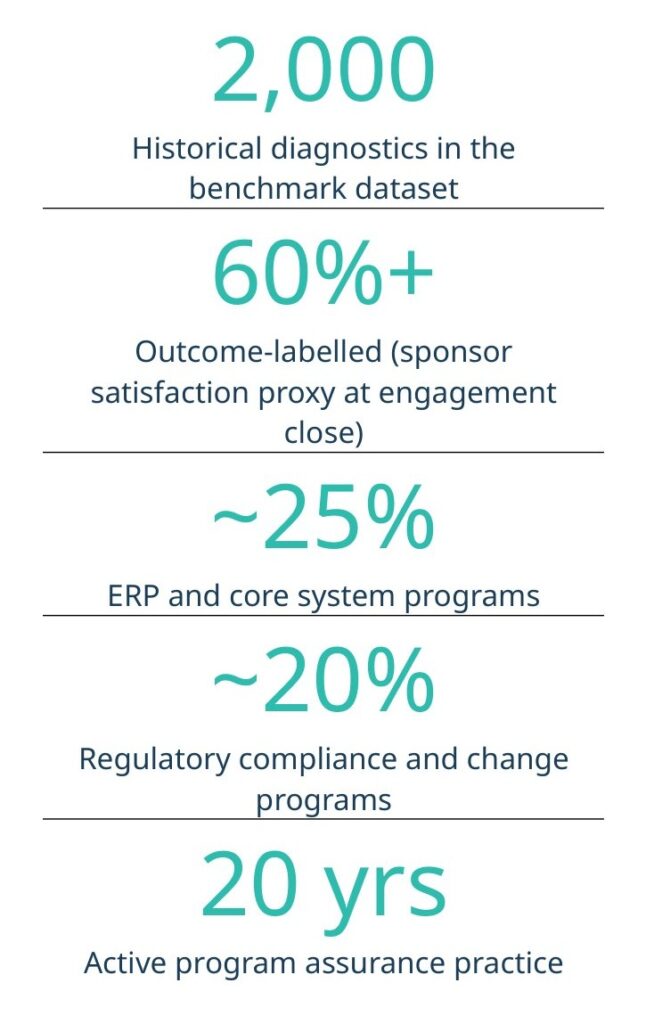
The benchmark dataset draws on 2,000+ diagnostics conducted over 20 years of program assurance practice, with roughly a quarter in ERP and core systems and a fifth in regulatory change. Outcome data from 1,200 programs is coded against whether sponsors judged the program delivered to expectations and achieved its intended business outcomes. Statistical regression is applied to calculate correlations and confidence levels. Where cohort matching is thin, confidence intervals are widened and disclosed.
Every condition and recommendation in the report comes from the Recommendations Library — not generic maturity-model criteria, but interventions grounded in what governance forums actually needed to see at the gate across comparable programs. The methodology is standardised and versioned. Multi-respondent attestation corroborates the evidence base across roles. Independence guardrails are published, scoring is robust and standardised, there are no contingent fees based on outcomes, and conflicts are disclosed. It is your documented due diligence.
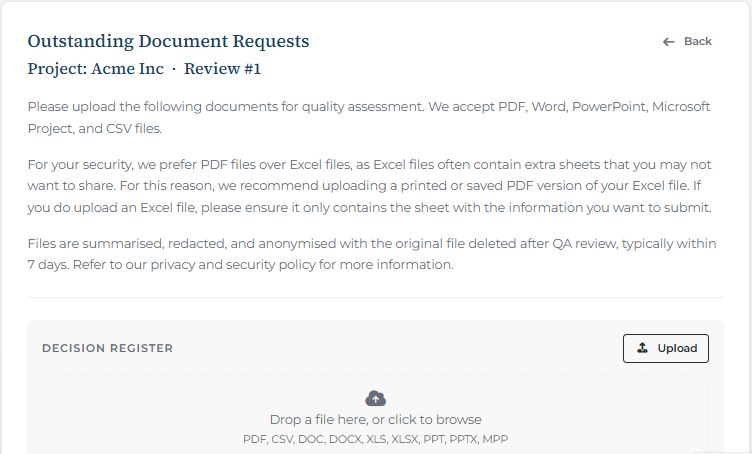
For organisations with security or procurement constraints, document uploads are optional — full diagnostic value is delivered without them — and data residency options cover AU, US, and EU.