You stake your reputation on managing risk, but delivery reporting is political and problems are hidden until they’re unrecoverable.
Independent project review at the speed you need for key decisions means you prevent failures, instead of dissecting them.
Three gaps boards face at the funding gate
Late discovery of risks that were knowable earlier. Material control gaps are frequently present at the time of the stage-gate review. They are not acted on because those gaps aren’t communicated, and no independent verification is applied. Further, most stage-gate reviews focus on delivery velocity, not business readiness. The signals were there — they were not surfaced.
Inconsistent, non-comparable reporting across programs. Status reporting uses subjective frameworks that vary between programs. RAG ratings are politically managed and not benchmarkable across the portfolio. Optimism bias degrades reporting as it moves up the chain of command, obscuring systemic issues behind programme-level summaries.
Traditional assurance that cannot match stage-gate timing. The traditional assurance approach is too slow, and too expensive. Reports are detailed and thorough but take four to eight weeks at $40,000 to $100,000 or more. That level of assurance cannot be commissioned at every material stage gate for every program – it’s suitable only for remediating identified issues or signing off on high risk programs. The gap between what full assurance costs and what stage gates require is where the decision record is weakest.
The Governance Decision Memo
The Governance Decision Memo is a formal, single-page artefact documenting:
- An assurance recommendation: proceed, where a step-up in discipline is required, or where a full assurance review is warranted.
- A risk rating with confidence basis, benchmarked against outcome data from 2,000+ comparable programs
- Conditions-to-proceed — forward-looking, manageable delivery actions with named owners
- Escalation questions for the next committee or steering forum
The Memo provides evidence that an independent, benchmarked assessment was applied before funding was released. Whether the program succeeds or not, the record documents what was assessed, what was found, what conditions were set, and what the recommendation was.
The Assurance Report
The diagnostic assesses delivery risk across multiple dimensions — business readiness, sponsorship quality, resourcing, and vendor performance alongside technical execution. Multiple stakeholders contribute independently, and each attests their inputs.
The output is an Assurance Report that benchmarks your program against a matched peer cohort — programs of comparable size, industry, category, and complexity — drawn from over 2,000 historical diagnostics. The benchmark shows how programs like yours actually performed in comparable situations. It gives you a reference frame for your business case assumptions that does not depend on the people who wrote the business case.
Within 72 hours of engagement, the ordering executive receives:
- Risk rating with confidence basis — not a binary pass/fail, but a graded assessment with the evidence and assumptions behind it disclosed
- Benchmark percentile — the program scored against a matched peer cohort by sector, type, size, and stage, drawn from outcome data across 2,000+ diagnostics
- Alignment Index — where stakeholder views diverge across risk dimensions, documented as a governance signal rather than a performance finding
- Top 5 risk drivers — linked to attested respondent inputs, not consultant opinion
- 90-day action plan — highest-lift interventions with named owners, timeframes, and acceptance criteria
- Benefits-at-risk indicator — flags where delivery risk threatens committed benefits realisation
- Business readiness assessment — evaluates whether the organisation is prepared to adopt the outcome, not just whether deliverables are on track
- Governance Decision Memo — a single-page decision artefact with recommended action, confidence level, and conditions-to-proceed, designed to circulate independently in board papers
The benchmark shows how programs like yours actually performed. Where internally-generated status shows confidence but comparable programs with similar control profiles delivered late, over budget, or wrote off benefits the report will flag this – a signal no steering committee can overlook.
The Assurance Panel RFP Pack
If the Governance Decision Memo and Assurance Report recommend further investigation of serious issues, ProjectPhD can product a full RFP document for sending to your panel of assurance providers. This document is tightly scoped to ensure a quality review that can be delivered quickly and efficiently.
If a full RFP process is not required, you can engage the experts behind ProjectPhD directly to conduct an in-person review backed by decades of experience and quantitative evaluation of project performance.
NOTE: The ProjectPhD tool, policies, and procedures are carefully designed to provide complete independence and neutrality. The tool will not recommend a review without a demonstrable requirement, and review scope and recommendations are framed per the RFP document above, to enable delivery by any consultant the client prefers. Methodology is shared with the report, so you can verify the findings are real and not shaped towards a particular outcome.
20-Year Empirical Record
The benchmark dataset draws on 2,000+ program diagnostics conducted over 20 years of assurance practice, with roughly a quarter in ERP and core systems and a fifth in regulatory change programs. Outcome data from 1,200 of those programs is coded against whether sponsors judged the program delivered to expectations and achieved its intended business outcomes. Every recommended condition is drawn from the ProjectPhD Recommendations Library — interventions grounded in what boards and committees actually needed to see at the funding gate, and what happened in programs where that evidence was absent.
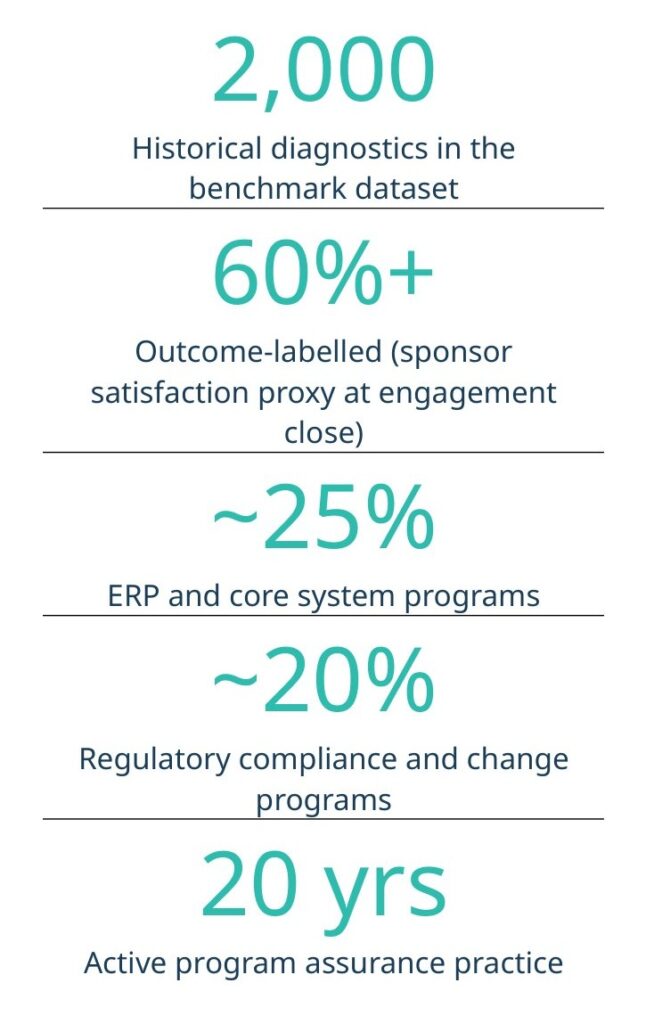
Every recommendation is grounded in 20 years of seeing what boards and sponsors actually needed — and what happened when they didn’t get it.
If the program delivers, the governance record confirms that appropriate independent controls were applied. If it does not, the record shows the committee acted on a documented, evidence-based, independently verified decision basis at the point of capital release. The methodology is designed to hold up under exactly the scrutiny that follows — post-incident review, external audit, or regulatory inquiry. That defensibility is not incidental. It is the primary design constraint. It is your documented due diligence.